SEC1215: From Zero to Agentic
Building Your First AI-Driven Threat Investigation in Splunk Enterprise Security
Splunk .Conf SEC1215
13:30 Tuesday 15th September 2026
Denver Conference Centre
Agentic AI promises autonomous security operations — but where do you actually start? This session cuts through the hype with hard-won lessons from building a bespoke agentic use case inside Splunk Enterprise Security from scratch. We cover LLM selection on a real-world budget, native Splunk integration patterns, and the critical pitfalls that cost time before delivering value. Practical, honest, and immediately applicable.
Takeaway 1
Choose the right LLM for SecOps — balancing cost, latency, privacy, and capability without defaulting to the biggest name.
Takeaway 2
A repeatable pattern to integrate agentic workflows into Splunk ES — what to build yourself vs. what Splunk gives you for free.
Takeaway 3
Avoid the top pitfalls — a prioritised starting framework for teams with limited time and budget to reach value fast.
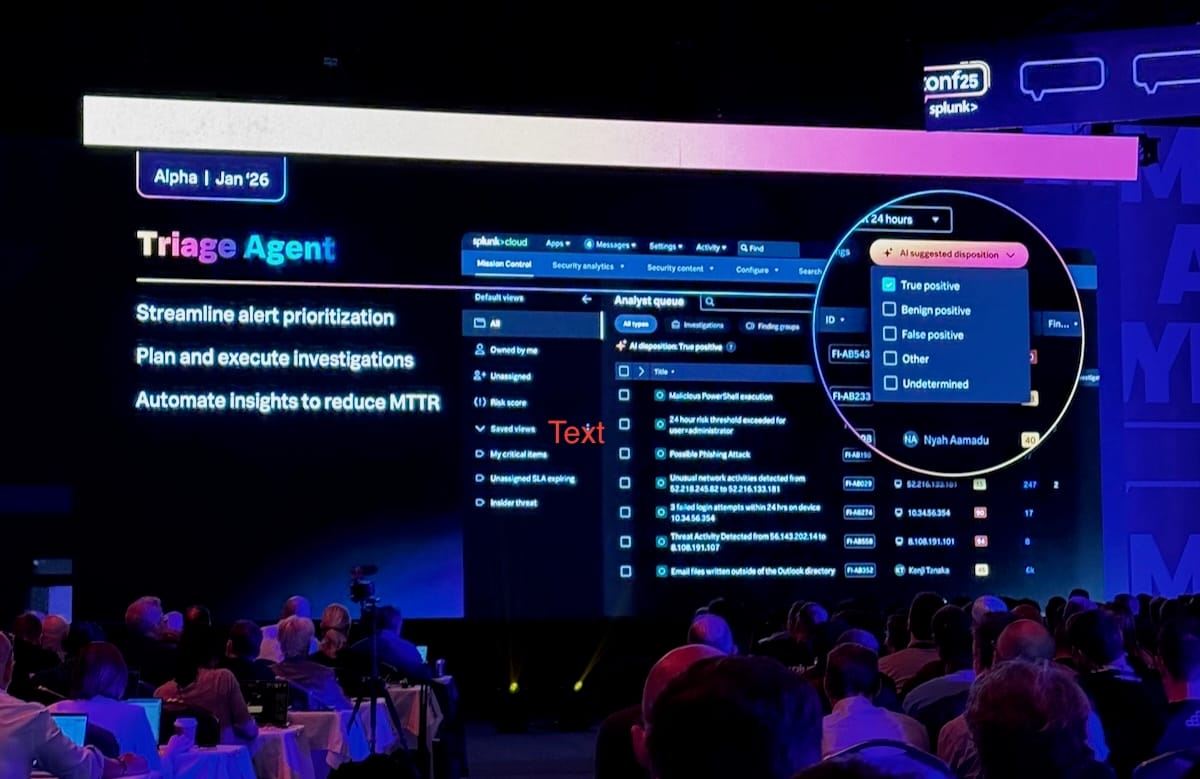
During this session we review how we built our first Agentic AI integration into Enterprise Security, the many pitfalls we discovered and our learning journey as we started our AI journey.
Come along and see how we developed our TA_ResponseActions Splunk App to connect to AI LLM engines.